Entra ID Device Registration with ROADtools Default OS Build
Identifies a Microsoft Entra ID device registration where the recorded cloud device operating system build is "10.0.19041.928" and the device display name follows the default "DESKTOP-" pattern. This combination is the default device profile that ROADtools (roadtx) uses when registering a device, and it is uncommon for the OS build to match the hardcoded value across an environment of otherwise patched hosts. Adversaries register rogue devices in Entra ID to acquire a Primary Refresh Token (PRT), establish persistence, and obtain trusted, programmatic access to the tenant. Because the OS build is a tool default, this is a high-fidelity but evadable indicator; baseline approved provisioning tooling and device naming conventions before relying on it. This rule also flags a device registration via Windows Hello for Business (WHfB) whose user agent carries the ROADtools hardcoded Dsreg build "10.0.19044.1826" ("Dsreg/10.0 (Windows 10.0.19044.1826)"), which is a separate tool tell from the device OS build and survives a change to the registered OS version or device name.
Elastic rule (View on GitHub)
  1[metadata]
  2creation_date = "2026/05/26"
  3integration = ["azure"]
  4maturity = "production"
  5updated_date = "2026/11/17"
  6
  7[rule]
  8author = ["Elastic"]
  9description = """
 10Identifies a Microsoft Entra ID device registration where the recorded cloud device operating system build is
 11"10.0.19041.928" and the device display name follows the default "DESKTOP-" pattern. This combination is the default
 12device profile that ROADtools (roadtx) uses when registering a device, and it is uncommon for the OS build to match the
 13hardcoded value across an environment of otherwise patched hosts. Adversaries register rogue devices in Entra ID to
 14acquire a Primary Refresh Token (PRT), establish persistence, and obtain trusted, programmatic access to the tenant.
 15Because the OS build is a tool default, this is a high-fidelity but evadable indicator; baseline approved provisioning
 16tooling and device naming conventions before relying on it. This rule also flags a device registration via Windows Hello
 17for Business (WHfB) whose user agent carries the ROADtools hardcoded Dsreg build "10.0.19044.1826" ("Dsreg/10.0 (Windows
 1810.0.19044.1826)"), which is a separate tool tell from the device OS build and survives a change to the registered OS
 19version or device name.
 20"""
 21false_positives = [
 22    """
 23    Legitimate device registrations may coincidentally use the `10.0.19041.928` build (Windows 10 20H1) with a default
 24    `DESKTOP-` hostname, particularly on imaged or unmanaged Windows hosts that have not been updated. Validate against
 25    your device inventory, expected provisioning workflows, and the registering user before escalating.
 26    """,
 27    """
 28    Authorized red team or penetration testing engagements that use ROADtools to register devices will match this rule.
 29    If this is expected, add exceptions for the specific user principal names, source IPs, or device names involved.
 30    """,
 31    """
 32    A genuine native Windows device-registration client (Dsreg) running on a host that is actually on build
 33    `10.0.19044.1826` (Windows 10 21H2) will present the same user agent. Validate the host's real build and the
 34    registration source; the hardcoded `10.0.19044.1826` value repeating across registrations is the tool tell.
 35    """,
 36]
 37from = "now-9m"
 38index = ["logs-azure.auditlogs-*"]
 39language = "kuery"
 40license = "Elastic License v2"
 41name = "Entra ID Device Registration with ROADtools Default OS Build"
 42note = """## Triage and analysis
 43
 44### Investigating Entra ID Device Registration with ROADtools Default OS Build
 45
 46ROADtools (roadtx) registers a device in Entra ID with a default cloud device OS build of `10.0.19041.928` and a default
 47display name of `DESKTOP-<8 random characters>`. This OS build is the current default value roadtx uses and
 48differs from the OS version of legitimate hosts, making the build a useful indicator of ROADtools device registration.
 49Rogue device registration is typically a precursor to Primary Refresh Token (PRT) acquisition, MFA/Conditional Access
 50bypass, and persistent token-based access.
 51
 52The matching Entra ID audit event is an `Add device` operation initiated by the `Device Registration Service`, where the
 53modified properties record the registered device characteristics:
 54
 55- `azure.auditlogs.properties.target_resources.0.modified_properties.3` (`CloudDeviceOSVersion`) = `10.0.19041.928`
 56- `azure.auditlogs.properties.target_resources.0.modified_properties.4` (`CloudDisplayName`) = `DESKTOP-*`
 57
 58### Possible investigation steps
 59
 60- Confirm the registering identity via `azure.auditlogs.properties.initiated_by.user.userPrincipalName` and determine
 61whether that user is expected to register a new device.
 62- Review `azure.auditlogs.identity` to confirm the `Device Registration Service` initiated the request, and use
 63`azure.correlation_id` to pivot across the full registration flow (`Add device`, `Add registered users to device`,
 64`Add registered owner to device`).
 65- Inspect the device name in `azure.auditlogs.properties.target_resources.0.display_name`; default `DESKTOP-` names that
 66do not match your naming convention are suspicious.
 67- Pivot to `azure.signinlogs` for the same user and timeframe and look for follow-on sign-ins where the incoming token
 68type is a `primaryRefreshToken`, or for risky/AiTM sign-ins immediately preceding the registration.
 69- Review `azure.auditlogs.properties.initiated_by.user.ipAddress` and geolocation for the registration source. Flag
 70unexpected IPs, hosting/VPS ASNs, or impossible-travel relative to the user's normal activity.
 71- Correlate with the user-agent-based device registration rules (e.g., `Dsreg/*`, `DeviceRegistrationClient`,
 72`Microsoft.OData.Client/*`) for the same user or correlation ID to strengthen attribution to ROADtools.
 73
 74### False positive analysis
 75
 76- Unmanaged or imaged Windows 10 20H1 hosts may legitimately present the `10.0.19041.928` build with a default
 77`DESKTOP-` hostname. Validate against device inventory and known provisioning programs.
 78- Authorized security assessments using ROADtools will match. Document the engagement and add scoped exceptions.
 79
 80### Response and remediation
 81
 82- If confirmed malicious, remove the registered device from Entra ID and revoke the user's refresh tokens and primary
 83refresh tokens.
 84- Disable the account or reset credentials per policy and review for additional persistence (added owners, app
 85registrations, or service principal credentials).
 86- Conduct historical analysis using `azure.correlation_id` and the registering user to determine scope of access.
 87- Tighten device registration and join controls via Conditional Access (restrict who can register/join devices and
 88require MFA for registration).
 89"""
 90references = [
 91    "https://unit42.paloaltonetworks.com/roadtools-cloud-attacks/",
 92    "https://github.com/dirkjanm/ROADtools",
 93    "https://dirkjanm.io/introducing-roadtools-token-exchange-roadtx/",
 94]
 95risk_score = 73
 96rule_id = "db1271cd-f574-4173-b4e5-7369f3c03d44"
 97severity = "high"
 98tags = [
 99    "Domain: Cloud",
100    "Domain: Identity",
101    "Data Source: Azure",
102    "Data Source: Microsoft Entra ID",
103    "Data Source: Microsoft Entra ID Audit Logs",
104    "Use Case: Identity and Access Audit",
105    "Use Case: Threat Detection",
106    "Tactic: Persistence",
107    "Resources: Investigation Guide",
108    "Noise: Unknown",
109    "Performance: Normal",
110    "Rule Type: Custom Query (KQL)",
111    "Platform: Entra ID",
112]
113timestamp_override = "event.ingested"
114type = "query"
115
116query = '''
117data_stream.dataset:"azure.auditlogs" and
118(
119   (
120    event.action:"Add device" and
121    azure.auditlogs.properties.target_resources.0.modified_properties.3.new_value:*10.0.19041.928* and
122    azure.auditlogs.properties.target_resources.0.modified_properties.4.new_value:*DESKTOP-*
123   ) or (
124    event.action: "Add Windows Hello for Business credential" and
125    azure.auditlogs.properties.userAgent: "Dsreg/10.0 (Windows 10.0.19044.1826)"
126 )
127)
128'''
129
130
131[[rule.threat]]
132framework = "MITRE ATT&CK"
133[[rule.threat.technique]]
134id = "T1098"
135name = "Account Manipulation"
136reference = "https://attack.mitre.org/techniques/T1098/"
137[[rule.threat.technique.subtechnique]]
138id = "T1098.005"
139name = "Device Registration"
140reference = "https://attack.mitre.org/techniques/T1098/005/"
141
142
143
144[rule.threat.tactic]
145id = "TA0003"
146name = "Persistence"
147reference = "https://attack.mitre.org/tactics/TA0003/"
148
149[rule.investigation_fields]
150field_names = [
151    "@timestamp",
152    "event.action",
153    "event.outcome",
154    "azure.auditlogs.identity",
155    "azure.auditlogs.operation_name",
156    "azure.auditlogs.properties.target_resources.0.display_name",
157    "azure.auditlogs.properties.target_resources.0.modified_properties.3.new_value",
158    "azure.auditlogs.properties.target_resources.0.modified_properties.4.new_value",
159    "azure.auditlogs.properties.initiated_by.user.userPrincipalName",
160    "azure.auditlogs.properties.initiated_by.user.ipAddress",
161    "azure.auditlogs.properties.userAgent",
162    "azure.correlation_id",
163]
Triage and analysis
Investigating Entra ID Device Registration with ROADtools Default OS Build
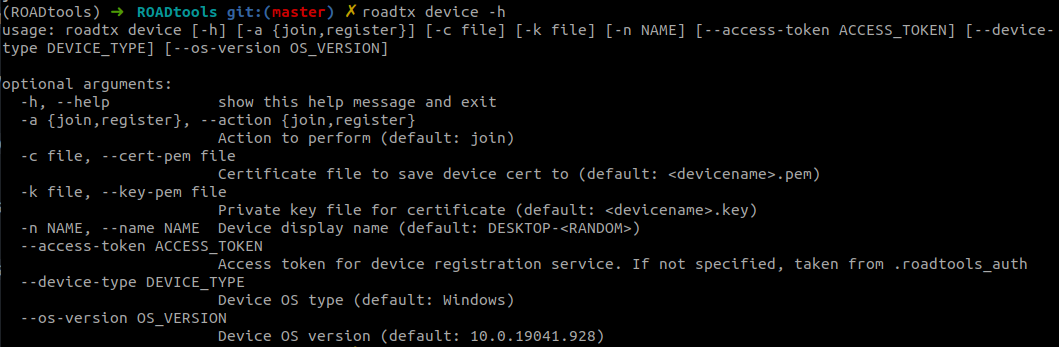
ROADtools (roadtx) registers a device in Entra ID with a default cloud device OS build of 10.0.19041.928 and a default
display name of DESKTOP-<8 random characters>. This OS build is the current default value roadtx uses and
differs from the OS version of legitimate hosts, making the build a useful indicator of ROADtools device registration.
Rogue device registration is typically a precursor to Primary Refresh Token (PRT) acquisition, MFA/Conditional Access
bypass, and persistent token-based access.
The matching Entra ID audit event is an Add device operation initiated by the Device Registration Service, where the
modified properties record the registered device characteristics:
azure.auditlogs.properties.target_resources.0.modified_properties.3(CloudDeviceOSVersion) =10.0.19041.928azure.auditlogs.properties.target_resources.0.modified_properties.4(CloudDisplayName) =DESKTOP-*
Possible investigation steps
- Confirm the registering identity via
azure.auditlogs.properties.initiated_by.user.userPrincipalNameand determine whether that user is expected to register a new device. - Review
azure.auditlogs.identityto confirm theDevice Registration Serviceinitiated the request, and useazure.correlation_idto pivot across the full registration flow (Add device,Add registered users to device,Add registered owner to device). - Inspect the device name in
azure.auditlogs.properties.target_resources.0.display_name; defaultDESKTOP-names that do not match your naming convention are suspicious. - Pivot to
azure.signinlogsfor the same user and timeframe and look for follow-on sign-ins where the incoming token type is aprimaryRefreshToken, or for risky/AiTM sign-ins immediately preceding the registration. - Review
azure.auditlogs.properties.initiated_by.user.ipAddressand geolocation for the registration source. Flag unexpected IPs, hosting/VPS ASNs, or impossible-travel relative to the user's normal activity. - Correlate with the user-agent-based device registration rules (e.g.,
Dsreg/*,DeviceRegistrationClient,Microsoft.OData.Client/*) for the same user or correlation ID to strengthen attribution to ROADtools.
False positive analysis
- Unmanaged or imaged Windows 10 20H1 hosts may legitimately present the
10.0.19041.928build with a defaultDESKTOP-hostname. Validate against device inventory and known provisioning programs. - Authorized security assessments using ROADtools will match. Document the engagement and add scoped exceptions.
Response and remediation
- If confirmed malicious, remove the registered device from Entra ID and revoke the user's refresh tokens and primary refresh tokens.
- Disable the account or reset credentials per policy and review for additional persistence (added owners, app registrations, or service principal credentials).
- Conduct historical analysis using
azure.correlation_idand the registering user to determine scope of access. - Tighten device registration and join controls via Conditional Access (restrict who can register/join devices and require MFA for registration).
References
-
Open-source framework ROADtools is being misused by threat actors for cloud intrusions. Learn how to identify its malicious use.
Read More -
A collection of Azure AD/Entra tools for offensive and defensive security purposes - dirkjanm/ROADtools
Read More -
Ever since the initial release of ROADrecon and the ROADtools framework I have been adding new features to it, especially on the authentication side. As a result, it supports many forms of authentication, such as using Primary Refresh Tokens (PRTs), PRT cookies, and regular access/refresh tokens. The authentication modules are all part of the shared library roadlib, and can be used in other tools by importing the library. Even though you can request tokens for any Azure AD connected resource and with many client IDs, the only tool exposing this authentication part was ROADrecon. It always felt unnatural and illogical to tell people that you can use a recon tool to request tokens for many other purposes. So I decided to start writing a new tool, which resolves around requesting and using Azure AD tokens. As I was working on this, I started adding proof of concepts I wrote during my Azure AD devices research into the tool, adding support for registering devices and requesting Primary Refresh Tokens using device credentials. I also added various modules for injecting PRTs into browser sessions with Selenium, and for automating authentication with MFA. The result is a comprehensive tool called ROADtools Token eXchange, or simply roadtx. Currently it has the following capabilities:
Read More
Related rules
- Entra ID Device Registration with Phishing Kit Default OS Build
- Entra ID AiTM Phishing-Kit Chain Detected
- Entra ID Guest Account Promoted to Member
- Entra ID Kali365 Default User-Agent Detected
- Entra ID Multiple Device Registrations by a Single User