New GitHub Self Hosted Action Runner
This rule detects the registration of a self-hosted GitHub Actions runner by a user and source ASN (autonomous system) pair not seen in the last 5 days. The source IP is resolved to its ASN at query time, so address churn inside the same ISP or cloud provider does not produce new alerts. Adversaries may abuse self-hosted runners to execute workflow jobs on customer infrastructure.
Elastic rule (View on GitHub)
  1[metadata]
  2creation_date = "2025/11/28"
  3integration = ["github"]
  4maturity = "production"
  5min_stack_comments = "ES|QL IP_LOCATION requires 9.5.0+."
  6min_stack_version = "9.5.0"
  7updated_date = "2026/10/07"
  8
  9[rule]
 10author = ["Elastic"]
 11description = """
 12This rule detects the registration of a self-hosted GitHub Actions runner by a user and source ASN (autonomous
 13system) pair not seen in the last 5 days. The source IP is resolved to its ASN at query time, so address churn inside
 14the same ISP or cloud provider does not produce new alerts. Adversaries may abuse self-hosted runners to execute
 15workflow jobs on customer infrastructure.
 16"""
 17false_positives = [
 18    "Authorized self-hosted GitHub actions runner.",
 19]
 20from = "now-7205m"
 21interval = "5m"
 22language = "esql"
 23license = "Elastic License v2"
 24name = "New GitHub Self Hosted Action Runner"
 25note = """## Triage and analysis
 26
 27### Investigating New GitHub Self Hosted Action Runner
 28
 29Adversaries who gain the ability to modify or trigger workflows in a linked GitHub repository can execute arbitrary commands on the runner host.
 30
 31### Possible investigation steps
 32
 33- Validate the user is authoried to perform this change
 34- Review the purpose of the self-hosted action runner and what actions will be executed.
 35- Verify if there is any adjascent  sensitive file access or collection.
 36- Correlate with other alerts and investiguate if this activity is related to a supply chain attack.
 37
 38### False positive analysis
 39
 40- Authorized github self-hosted actions runner.
 41
 42### Response and remediation
 43
 44- Immediately isolate the affected system from the network to prevent further unauthorized command execution and potential lateral movement.
 45- Terminate any suspicious child processes that were initiated by the Github actions runner.
 46- Conduct a thorough review of the affected system's logs and configurations to identify any unauthorized changes or additional indicators of compromise.
 47- Restore the system from a known good backup if any unauthorized changes or malicious activities are confirmed.
 48- Implement application whitelisting to prevent unauthorized execution.
 49- Escalate the incident to the security operations center (SOC) or incident response team for further investigation and to assess the potential impact on the broader network."""
 50references = [
 51    "https://www.elastic.co/blog/shai-hulud-worm-npm-supply-chain-compromise",
 52    "https://socket.dev/blog/shai-hulud-strikes-again-v2",
 53    "https://www.wiz.io/blog/shai-hulud-2-0-ongoing-supply-chain-attack"
 54]
 55risk_score = 47
 56rule_id = "40c34c8a-b0bc-43bc-83aa-d2b76bf129e1"
 57severity = "medium"
 58tags = [
 59    "Domain: Cloud",
 60    "Use Case: Threat Detection",
 61    "Tactic: Initial Access",
 62    "Data Source: Github",
 63    "Data Source: GitHub Audit Logs",
 64    "Resources: Investigation Guide",
 65    "Noise: Low",
 66    "Performance: Fast",
 67    "Profile: Recommended",
 68    "Threat: Supply Chain",
 69    "Rule Type: ES|QL",
 70    "Platform: GitHub",
 71    "Domain: SaaS",
 72]
 73timestamp_override = "event.ingested"
 74type = "esql"
 75
 76query = '''
 77FROM logs-github.audit-*
 78| WHERE event.dataset == "github.audit" AND event.category == "configuration"
 79  AND event.action IN ("repo.register_self_hosted_runner", "org.register_self_hosted_runner", "enterprise.register_self_hosted_runner")
 80  AND user.name IS NOT NULL AND github.actor_ip IS NOT NULL
 81| IP_LOCATION asn = github.actor_ip WITH { "database_file": "GeoLite2-ASN.mmdb", "properties": ["asn", "organization_name"] }
 82| IP_LOCATION geo = github.actor_ip WITH { "properties": ["country_iso_code"] }
 83| WHERE asn.asn IS NOT NULL
 84| STATS Esql.event_count = COUNT(*),
 85        Esql.first_seen = MIN(@timestamp),
 86        Esql.last_seen = MAX(@timestamp),
 87        Esql.ip_values = VALUES(github.actor_ip),
 88        Esql.event_action_values = VALUES(event.action),
 89        Esql.repo_values = VALUES(github.repo),
 90        Esql.org_values = VALUES(github.org),
 91        Esql.country_values = VALUES(geo.country_iso_code),
 92        Esql.user_agent_values = VALUES(github.user_agent)
 93  BY user.name, asn.asn, asn.organization_name
 94// The 5-day history is the rule look-back (from = now-7205m). A user/ASN pair is new when its first
 95// event falls inside the current interval; the 10m bound allows for the 5m interval plus scheduling drift.
 96| WHERE DATE_DIFF("minute", Esql.first_seen, NOW()) <= 10
 97| EVAL Esql.source_as_number = asn.asn, Esql.source_as_organization_name = asn.organization_name
 98| KEEP user.name, Esql.*
 99'''
100
101[[rule.threat]]
102framework = "MITRE ATT&CK"
103
104[[rule.threat.technique]]
105id = "T1195"
106name = "Supply Chain Compromise"
107reference = "https://attack.mitre.org/techniques/T1195/"
108
109[[rule.threat.technique.subtechnique]]
110id = "T1195.001"
111name = "Compromise Software Dependencies and Development Tools"
112reference = "https://attack.mitre.org/techniques/T1195/001/"
113
114[[rule.threat.technique.subtechnique]]
115id = "T1195.002"
116name = "Compromise Software Supply Chain"
117reference = "https://attack.mitre.org/techniques/T1195/002/"
118
119[rule.threat.tactic]
120id = "TA0001"
121name = "Initial Access"
122reference = "https://attack.mitre.org/tactics/TA0001/"
Triage and analysis
Investigating New GitHub Self Hosted Action Runner
Adversaries who gain the ability to modify or trigger workflows in a linked GitHub repository can execute arbitrary commands on the runner host.
Possible investigation steps
- Validate the user is authoried to perform this change
- Review the purpose of the self-hosted action runner and what actions will be executed.
- Verify if there is any adjascent sensitive file access or collection.
- Correlate with other alerts and investiguate if this activity is related to a supply chain attack.
False positive analysis
- Authorized github self-hosted actions runner.
Response and remediation
- Immediately isolate the affected system from the network to prevent further unauthorized command execution and potential lateral movement.
- Terminate any suspicious child processes that were initiated by the Github actions runner.
- Conduct a thorough review of the affected system's logs and configurations to identify any unauthorized changes or additional indicators of compromise.
- Restore the system from a known good backup if any unauthorized changes or malicious activities are confirmed.
- Implement application whitelisting to prevent unauthorized execution.
- Escalate the incident to the security operations center (SOC) or incident response team for further investigation and to assess the potential impact on the broader network.
References
-
Certain npm packages were infected with self-replicating malware known as the "Shai-Hulud” worm. At this time, Elastic has found no evidence of compromise within Elastic’s software environment. Learn ...
Read More -
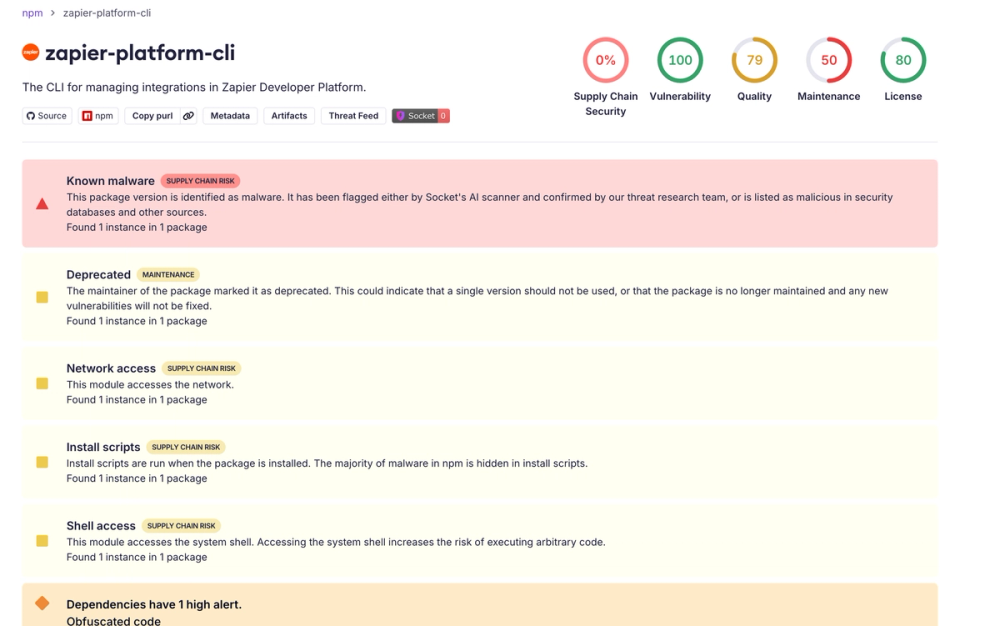
Another wave of Shai-Hulud campaign has hit npm with more than 500 packages and 700+ versions affected.
Read More -
Shai-Hulud is back, spreading an npm malware worm through thousands of GitHub repos. Learn the impact, attacker methods, and how to defend your supply chain.
Read More
Related rules
- GitHub Actions Workflow Modification Blocked
- GitHub Activity on a Private Repository from an Unusual ASN
- GitHub Actions Unusual Bot Push to Repository
- High Number of Closed Pull Requests by User
- Several Failed Protected Branch Force Pushes by User