GKE Service Account Modified RBAC Objects
Detects write operations performed by GKE service accounts against RBAC resources (Roles, ClusterRoles, RoleBindings, ClusterRoleBindings). Service accounts typically do not manage RBAC directly; this activity may indicate token abuse or unauthorized privilege escalation.
Elastic rule (View on GitHub)
  1[metadata]
  2creation_date = "2026/07/10"
  3integration = ["gcp"]
  4maturity = "production"
  5updated_date = "2026/09/18"
  6
  7[rule]
  8author = ["Elastic"]
  9description = """
 10Detects write operations performed by GKE service accounts against RBAC resources (Roles, ClusterRoles, RoleBindings,
 11ClusterRoleBindings). Service accounts typically do not manage RBAC directly; this activity may indicate token abuse or
 12unauthorized privilege escalation.
 13"""
 14false_positives = [
 15    """
 16    In-cluster controllers, operators, and CI jobs may legitimately reconcile RBAC manifests. Baseline known automation
 17    service accounts before tuning.
 18    """,
 19]
 20from = "now-6m"
 21index = ["logs-gcp.audit-*"]
 22language = "kuery"
 23license = "Elastic License v2"
 24name = "GKE Service Account Modified RBAC Objects"
 25note = """## Triage and analysis
 26
 27### Investigating GKE Service Account Modified RBAC Objects
 28
 29This rule detects service accounts performing allowed write actions on RBAC resources. Stolen or over-privileged service
 30account tokens can silently alter authorization to gain or retain elevated access.
 31
 32### Possible investigation steps
 33
 34- Review `client.user.email`, `event.action`, and `gcp.audit.resource_name`.
 35- Trace the acting service account to its owning workload and inspect recent image changes or exec activity.
 36- Correlate with change tickets or GitOps commits for the same RBAC object.
 37
 38### False positive analysis
 39
 40- Platform operators and GitOps controllers running in-cluster commonly create or patch RBAC objects.
 41
 42### Response and remediation
 43
 44- Revert unauthorized RBAC changes, rotate the service account credentials, and tighten RBAC for the workload.
 45
 46"""
 47setup = "The GCP Fleet integration with GKE audit logs enabled is required to be compatible with this rule."
 48references = [
 49    "https://kubernetes.io/docs/reference/access-authn-authz/rbac/",
 50    "https://heilancoos.github.io/research/2025/12/16/kubernetes.html#overly-permissive-role-based-access-control",
 51]
 52risk_score = 47
 53rule_id = "c41e9854-3df3-465a-8234-4d625084ff86"
 54severity = "medium"
 55tags = [
 56    "Domain: Cloud",
 57    "Domain: Kubernetes",
 58    "Data Source: GCP",
 59    "Data Source: Google Cloud Platform",
 60    "Use Case: Threat Detection",
 61    "Tactic: Privilege Escalation",
 62    "Tactic: Persistence",
 63    "Resources: Investigation Guide",
 64    "Noise: Low",
 65    "Performance: Fast",
 66    "Rule Type: Custom Query (KQL)",
 67    "Platform: GCP",
 68    "Domain: Containers",
 69    "Platform: Kubernetes",
 70]
 71timestamp_override = "event.ingested"
 72type = "query"
 73
 74query = '''
 75data_stream.dataset:gcp.audit and service.name:"k8s.io" and event.outcome:success and
 76client.user.email:(system\:serviceaccount\:* and not (
 77  "system:serviceaccount:kube-system:clusterrole-aggregation-controller" or
 78  "system:serviceaccount:kube-system:generic-garbage-collector"
 79)) and event.action:(
 80  "io.k8s.authorization.rbac.v1.clusterrolebindings.create" or
 81  "io.k8s.authorization.rbac.v1.clusterrolebindings.delete" or
 82  "io.k8s.authorization.rbac.v1.clusterrolebindings.patch" or
 83  "io.k8s.authorization.rbac.v1.clusterrolebindings.update" or
 84  "io.k8s.authorization.rbac.v1.clusterroles.create" or
 85  "io.k8s.authorization.rbac.v1.clusterroles.delete" or
 86  "io.k8s.authorization.rbac.v1.clusterroles.patch" or
 87  "io.k8s.authorization.rbac.v1.clusterroles.update" or
 88  "io.k8s.authorization.rbac.v1.rolebindings.create" or
 89  "io.k8s.authorization.rbac.v1.rolebindings.delete" or
 90  "io.k8s.authorization.rbac.v1.rolebindings.patch" or
 91  "io.k8s.authorization.rbac.v1.rolebindings.update" or
 92  "io.k8s.authorization.rbac.v1.roles.create" or
 93  "io.k8s.authorization.rbac.v1.roles.delete" or
 94  "io.k8s.authorization.rbac.v1.roles.patch" or
 95  "io.k8s.authorization.rbac.v1.roles.update"
 96)
 97'''
 98
 99[[rule.threat]]
100framework = "MITRE ATT&CK"
101
102[[rule.threat.technique]]
103id = "T1098"
104name = "Account Manipulation"
105reference = "https://attack.mitre.org/techniques/T1098/"
106
107[[rule.threat.technique.subtechnique]]
108id = "T1098.006"
109name = "Additional Container Cluster Roles"
110reference = "https://attack.mitre.org/techniques/T1098/006/"
111
112[rule.threat.tactic]
113id = "TA0004"
114name = "Privilege Escalation"
115reference = "https://attack.mitre.org/tactics/TA0004/"
116
117[[rule.threat]]
118framework = "MITRE ATT&CK"
119
120[[rule.threat.technique]]
121id = "T1098"
122name = "Account Manipulation"
123reference = "https://attack.mitre.org/techniques/T1098/"
124
125[[rule.threat.technique.subtechnique]]
126id = "T1098.006"
127name = "Additional Container Cluster Roles"
128reference = "https://attack.mitre.org/techniques/T1098/006/"
129
130[rule.threat.tactic]
131id = "TA0003"
132name = "Persistence"
133reference = "https://attack.mitre.org/tactics/TA0003/"
134
135[rule.investigation_fields]
136field_names = [
137    "@timestamp",
138    "client.user.email",
139    "source.ip",
140    "user_agent.original",
141    "event.action",
142    "event.outcome",
143    "gcp.audit.resource_name",
144    "gcp.audit.request.kind",
145    "data_stream.namespace",
146]
Triage and analysis
Investigating GKE Service Account Modified RBAC Objects
This rule detects service accounts performing allowed write actions on RBAC resources. Stolen or over-privileged service account tokens can silently alter authorization to gain or retain elevated access.
Possible investigation steps
- Review
client.user.email,event.action, andgcp.audit.resource_name. - Trace the acting service account to its owning workload and inspect recent image changes or exec activity.
- Correlate with change tickets or GitOps commits for the same RBAC object.
False positive analysis
- Platform operators and GitOps controllers running in-cluster commonly create or patch RBAC objects.
Response and remediation
- Revert unauthorized RBAC changes, rotate the service account credentials, and tighten RBAC for the workload.
References
-

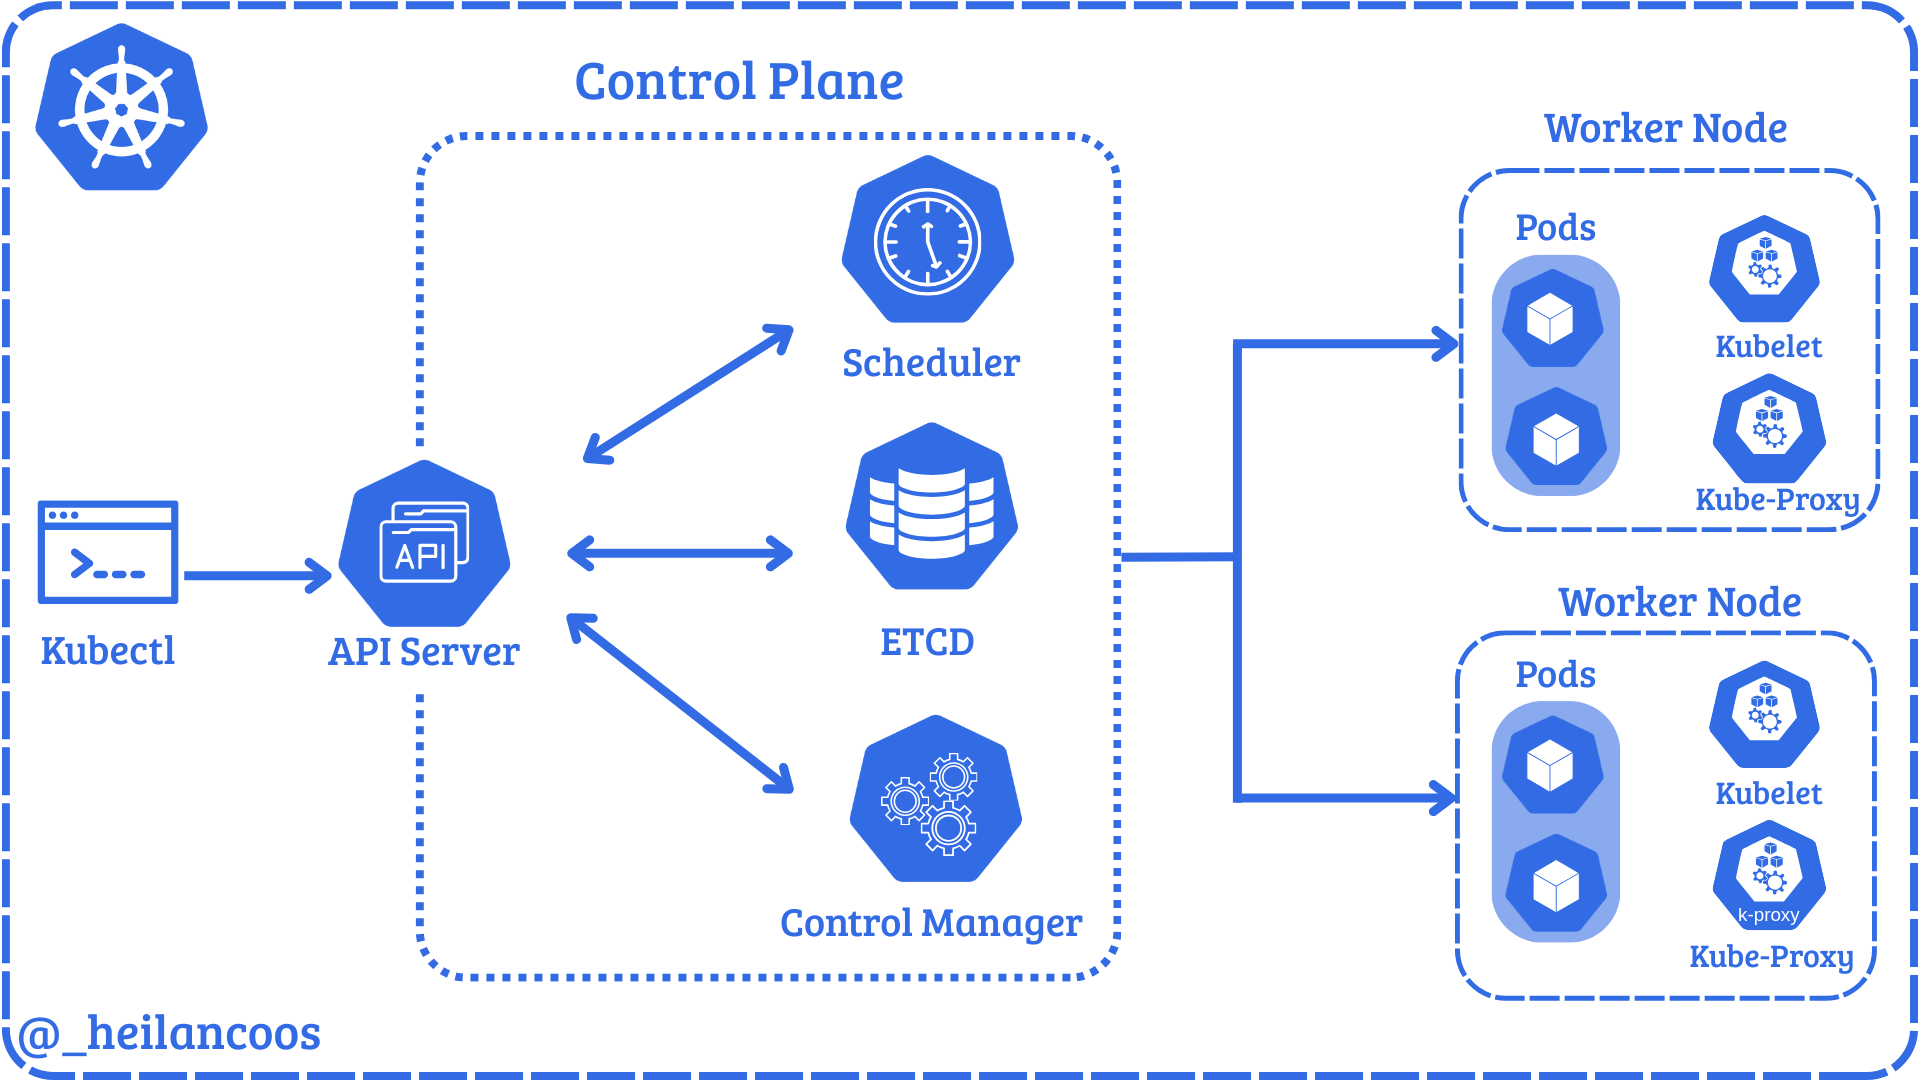
Role-based access control (RBAC) is a method of regulating access to computer or network resources based on the roles of individual users within your organization. RBAC authorization uses the rbac.authorization.k8s.io API group to drive authorization decisions, allowing you to dynamically configure policies through the Kubernetes API. To enable RBAC, start the API server with the --authorization-config flag set to a file that includes the RBAC authorizer; for example:
Read More -
Related rules
- GKE Creation of a RoleBinding Referencing a ServiceAccount
- GKE Creation or Modification of Sensitive Role
- GKE Certificate Signing Request API Client Signer Requested
- GKE Cluster-Admin Role Binding Created or Modified
- GKE API Request Impersonating Privileged Identity