GKE Creation or Modification of Sensitive Role
Detects creation or modification of GKE Roles or ClusterRoles that grant high-risk permissions, such as wildcard access or RBAC escalation verbs (bind, escalate, impersonate), which may enable privilege escalation or unauthorized access within the cluster.
Elastic rule (View on GitHub)
  1[metadata]
  2creation_date = "2026/07/10"
  3integration = ["gcp"]
  4maturity = "production"
  5updated_date = "2026/09/18"
  6
  7[rule]
  8author = ["Elastic"]
  9description = """
 10Detects creation or modification of GKE Roles or ClusterRoles that grant high-risk permissions, such as wildcard
 11access or RBAC escalation verbs (bind, escalate, impersonate), which may enable privilege escalation or unauthorized
 12access within the cluster.
 13"""
 14false_positives = [
 15    """
 16    Platform installers, GitOps controllers, and RBAC refactoring may legitimately create roles with broad permissions.
 17    Baseline approved automation and tune exclusions for known operators.
 18    """,
 19]
 20from = "now-6m"
 21index = ["logs-gcp.audit-*"]
 22language = "kuery"
 23license = "Elastic License v2"
 24name = "GKE Creation or Modification of Sensitive Role"
 25note = """## Triage and analysis
 26
 27### Investigating GKE Creation or Modification of Sensitive Role
 28
 29This rule detects allowed create, update, or patch actions on Roles and ClusterRoles that introduce high-risk RBAC
 30permissions, including wildcard access and escalation verbs like bind, escalate, or impersonate.
 31
 32### Possible investigation steps
 33
 34- Identify `client.user.email`, `source.ip`, and `user_agent.original`.
 35- Review `gcp.audit.resource_name`, `event.action`, and `gcp.audit.request` for the changed role.
 36- Enumerate RoleBindings or ClusterRoleBindings that reference the role and hunt for follow-on secret or exec activity.
 37
 38### False positive analysis
 39
 40- GitOps or platform bootstrap may create broad roles during onboarding. `system:addon-manager` patch reconciliation on built-in Roles and ClusterRoles is excluded.
 41
 42### Response and remediation
 43
 44- Revert unauthorized roles, remove unexpected bindings, and restrict RBAC change permissions to governed pipelines.
 45
 46"""
 47setup = "The GCP Fleet integration with GKE audit logs enabled is required. Request body capture on RBAC resources is required."
 48references = [
 49    "https://kubernetes.io/docs/reference/access-authn-authz/rbac/",
 50    "https://heilancoos.github.io/research/2025/12/16/kubernetes.html#overly-permissive-role-based-access-control",
 51]
 52risk_score = 47
 53rule_id = "2af7f1d7-d02c-476f-a130-e17ea4e556e6"
 54severity = "medium"
 55tags = [
 56    "Domain: Cloud",
 57    "Domain: Kubernetes",
 58    "Data Source: GCP",
 59    "Data Source: Google Cloud Platform",
 60    "Use Case: Threat Detection",
 61    "Tactic: Persistence",
 62    "Tactic: Privilege Escalation",
 63    "Resources: Investigation Guide",
 64    "Noise: Low",
 65    "Performance: Fast",
 66    "Rule Type: Custom Query (KQL)",
 67    "Platform: GCP",
 68    "Domain: Containers",
 69    "Platform: Kubernetes",
 70]
 71timestamp_override = "event.ingested"
 72type = "query"
 73
 74query = '''
 75data_stream.dataset:gcp.audit and service.name:"k8s.io" and event.outcome:success and
 76event.action:(
 77  "io.k8s.authorization.rbac.v1.roles.create" or
 78  "io.k8s.authorization.rbac.v1.roles.update" or
 79  "io.k8s.authorization.rbac.v1.roles.patch" or
 80  "io.k8s.authorization.rbac.v1.clusterroles.create" or
 81  "io.k8s.authorization.rbac.v1.clusterroles.update" or
 82  "io.k8s.authorization.rbac.v1.clusterroles.patch"
 83) and not source.ip:("::1" or "127.0.0.1") and not (
 84  client.user.email:"system:serviceaccount:kube-system:clusterrole-aggregation-controller" and
 85  gcp.audit.request.metadata.name:(admin or edit) and
 86  event.action:"io.k8s.authorization.rbac.v1.clusterroles.patch"
 87) and not (
 88  client.user.email:"system:addon-manager" and
 89  event.action:(
 90    "io.k8s.authorization.rbac.v1.roles.patch" or
 91    "io.k8s.authorization.rbac.v1.clusterroles.patch"
 92  )
 93) and (
 94  gcp.audit.request.rules.verbs:("*" or escalate or bind or impersonate) or
 95  (
 96    gcp.audit.request.rules.verbs:("*" or create or patch or update) and
 97    gcp.audit.request.rules.resources:(
 98      "*" or clusterroles or clusterrolebindings or roles or rolebindings or
 99      pods/exec or serviceaccounts/token or nodes/proxy or daemonsets
100    )
101  ) or
102  (
103    gcp.audit.request.rules.verbs:("*" or get or list) and
104    gcp.audit.request.rules.resources:("*" or secrets)
105  ) or
106  gcp.audit.response.rules.verbs:("*" or escalate or bind or impersonate) or
107  (
108    gcp.audit.response.rules.verbs:("*" or create or patch or update) and
109    gcp.audit.response.rules.resources:(
110      "*" or clusterroles or clusterrolebindings or roles or rolebindings or
111      pods/exec or serviceaccounts/token or nodes/proxy or daemonsets
112    )
113  ) or
114  (
115    gcp.audit.response.rules.verbs:("*" or get or list) and
116    gcp.audit.response.rules.resources:("*" or secrets)
117  )
118)
119'''
120
121[[rule.threat]]
122framework = "MITRE ATT&CK"
123
124[[rule.threat.technique]]
125id = "T1098"
126name = "Account Manipulation"
127reference = "https://attack.mitre.org/techniques/T1098/"
128
129[[rule.threat.technique.subtechnique]]
130id = "T1098.006"
131name = "Additional Container Cluster Roles"
132reference = "https://attack.mitre.org/techniques/T1098/006/"
133
134[rule.threat.tactic]
135id = "TA0003"
136name = "Persistence"
137reference = "https://attack.mitre.org/tactics/TA0003/"
138
139[[rule.threat]]
140framework = "MITRE ATT&CK"
141
142[[rule.threat.technique]]
143id = "T1098"
144name = "Account Manipulation"
145reference = "https://attack.mitre.org/techniques/T1098/"
146
147[[rule.threat.technique.subtechnique]]
148id = "T1098.006"
149name = "Additional Container Cluster Roles"
150reference = "https://attack.mitre.org/techniques/T1098/006/"
151
152[rule.threat.tactic]
153id = "TA0004"
154name = "Privilege Escalation"
155reference = "https://attack.mitre.org/tactics/TA0004/"
156
157[rule.investigation_fields]
158field_names = [
159    "@timestamp",
160    "client.user.email",
161    "source.ip",
162    "user_agent.original",
163    "event.action",
164    "event.outcome",
165    "gcp.audit.resource_name",
166    "gcp.audit.request.kind",
167    "data_stream.namespace",
168]
Triage and analysis
Investigating GKE Creation or Modification of Sensitive Role
This rule detects allowed create, update, or patch actions on Roles and ClusterRoles that introduce high-risk RBAC permissions, including wildcard access and escalation verbs like bind, escalate, or impersonate.
Possible investigation steps
- Identify
client.user.email,source.ip, anduser_agent.original. - Review
gcp.audit.resource_name,event.action, andgcp.audit.requestfor the changed role. - Enumerate RoleBindings or ClusterRoleBindings that reference the role and hunt for follow-on secret or exec activity.
False positive analysis
- GitOps or platform bootstrap may create broad roles during onboarding.
system:addon-managerpatch reconciliation on built-in Roles and ClusterRoles is excluded.
Response and remediation
- Revert unauthorized roles, remove unexpected bindings, and restrict RBAC change permissions to governed pipelines.
References
-

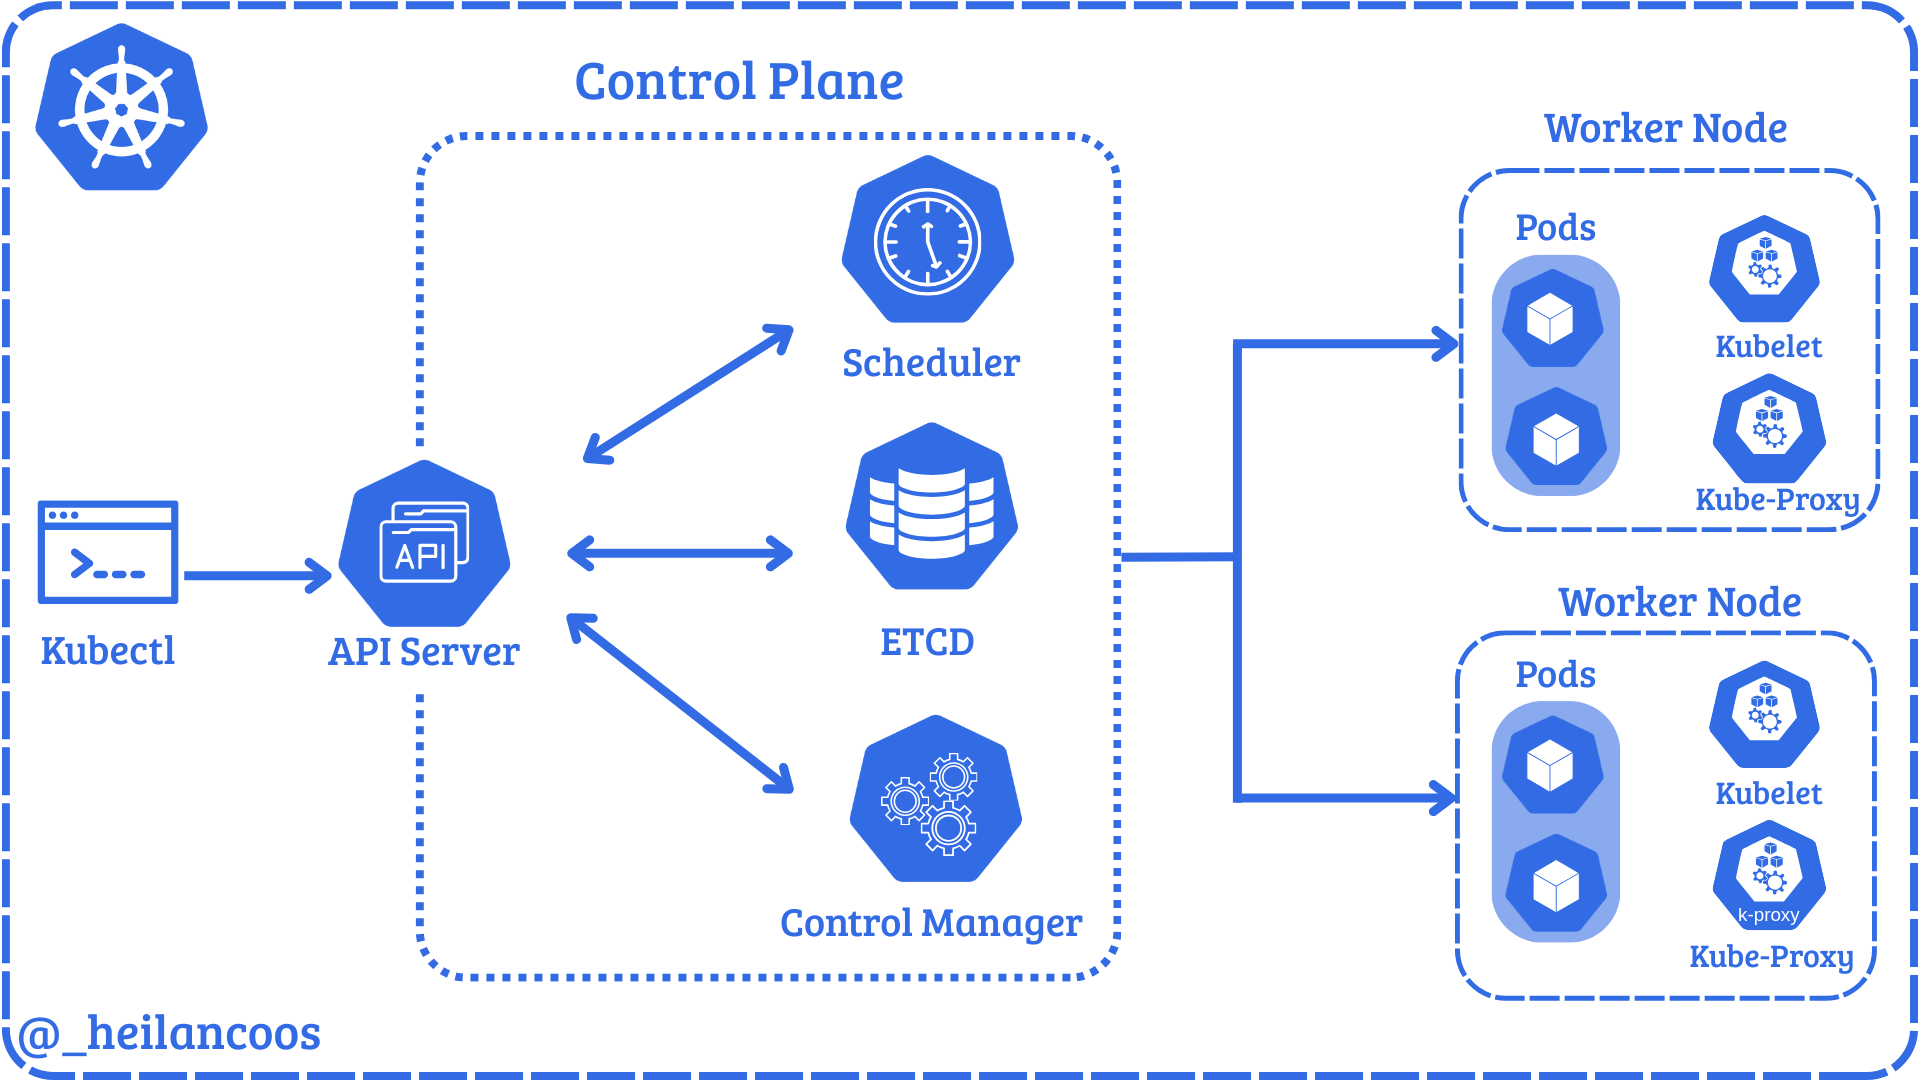
Role-based access control (RBAC) is a method of regulating access to computer or network resources based on the roles of individual users within your organization. RBAC authorization uses the rbac.authorization.k8s.io API group to drive authorization decisions, allowing you to dynamically configure policies through the Kubernetes API. To enable RBAC, start the API server with the --authorization-config flag set to a file that includes the RBAC authorizer; for example:
Read More -
Related rules
- GKE Creation of a RoleBinding Referencing a ServiceAccount
- GKE Service Account Modified RBAC Objects
- GKE Certificate Signing Request API Client Signer Requested
- GKE Cluster-Admin Role Binding Created or Modified
- GKE API Request Impersonating Privileged Identity