Entra ID Potential AiTM Sign-In via OfficeHome (Tycoon2FA)
Detects Microsoft Entra ID sign-ins consistent with Tycoon2FA phishing-as-a-service (PhaaS) adversary-in-the-middle (AiTM) activity: the Microsoft Authentication Broker requesting tokens for Microsoft Graph or Exchange Online, or the Office web client application authenticating to itself, combined with Node.js-style user agents (node, axios, undici). Tycoon 2FA bypasses MFA by relaying authentication and capturing session material, often targeting Microsoft 365 and Gmail. Baseline legitimate automation and developer tooling before tuning.
Elastic rule (View on GitHub)
  1[metadata]
  2creation_date = "2026/05/14"
  3integration = ["azure"]
  4maturity = "production"
  5updated_date = "2026/09/18"
  6
  7[rule]
  8author = ["Elastic"]
  9description = """
 10Detects Microsoft Entra ID sign-ins consistent with Tycoon2FA phishing-as-a-service (PhaaS) adversary-in-the-middle
 11(AiTM) activity: the Microsoft Authentication Broker requesting tokens for Microsoft Graph or Exchange Online, or the
 12Office web client application authenticating to itself, combined with Node.js-style user agents (node, axios, undici).
 13Tycoon 2FA bypasses MFA by relaying authentication and capturing session material, often targeting Microsoft 365 and
 14Gmail. Baseline legitimate automation and developer tooling before tuning.
 15"""
 16false_positives = [
 17    """
 18    Legitimate Node.js or undici-based automation, health checks, or internal services that use the Microsoft
 19    Authentication Broker or the same first-party application IDs against Graph or Exchange may match. Developers using
 20    axios or undici with delegated flows can also resemble this pattern.
 21    """,
 22]
 23from = "now-9m"
 24index = ["logs-azure.signinlogs-*"]
 25language = "kuery"
 26license = "Elastic License v2"
 27name = "Entra ID Potential AiTM Sign-In via OfficeHome (Tycoon2FA)"
 28note = """## Triage and analysis
 29
 30### Investigating Entra ID Potential AiTM Sign-In via OfficeHome (Tycoon2FA)
 31
 32Review user.name, azure.signinlogs.properties.user_principal_name, azure.signinlogs.properties.app_id,
 33azure.signinlogs.properties.resource_id, user_agent.original, source.ip, source.geo fields, and
 34azure.signinlogs.properties.session_id.
 35
 36Confirm whether the user intentionally signed in and whether Node.js-style user agents (node, axios, undici) are
 37expected for Microsoft Authentication Broker or Office web client flows in your environment.
 38
 39### Possible investigation steps
 40
 41- Correlate the session with Microsoft Graph activity logs and mailbox audit for follow-on data access.
 42- Review conditional access outcomes and MFA detail for the same session.
 43- Hunt for other sign-ins from the same source IP with unusual user agents or rapid OAuth patterns.
 44
 45### Response and remediation
 46
 47- If malicious, revoke refresh tokens for the user, reset credentials per policy, and review application consent.
 48- Block or monitor the source IP and escalate per incident procedures.
 49"""
 50references = ["https://any.run/malware-trends/tycoon/"]
 51risk_score = 73
 52rule_id = "6e6376c1-a71e-4789-a795-198b05664064"
 53severity = "high"
 54tags = [
 55    "Domain: Cloud",
 56    "Domain: Identity",
 57    "Data Source: Azure",
 58    "Data Source: Microsoft Entra ID",
 59    "Data Source: Microsoft Entra ID Sign-In Logs",
 60    "Use Case: Threat Detection",
 61    "Threat: Tycoon2FA",
 62    "Tactic: Initial Access",
 63    "Tactic: Credential Access",
 64    "Resources: Investigation Guide",
 65    "Noise: High",
 66    "Performance: Normal",
 67    "Profile: Aggressive",
 68    "Threat: AiTM Phishing",
 69    "Rule Type: Custom Query (KQL)",
 70    "Platform: Entra ID",
 71]
 72timestamp_override = "event.ingested"
 73type = "query"
 74query = '''
 75data_stream.dataset:"azure.signinlogs" and event.category:"authentication" and
 76event.action:"Sign-in activity" and
 77(
 78    (
 79        azure.signinlogs.properties.app_id:"29d9ed98-a469-4536-ade2-f981bc1d605e" and
 80        azure.signinlogs.properties.resource_id:(
 81            "00000002-0000-0ff1-ce00-000000000000" or "00000003-0000-0000-c000-000000000000"
 82        )
 83    ) or
 84    (
 85        azure.signinlogs.properties.app_id:"4765445b-32c6-49b0-83e6-1d93765276ca" and
 86        azure.signinlogs.properties.resource_id:"4765445b-32c6-49b0-83e6-1d93765276ca"
 87    )
 88) and user_agent.original:(node or axios* or undici)
 89'''
 90
 91[rule.investigation_fields]
 92field_names = [
 93    "@timestamp",
 94    "user.name",
 95    "user_agent.original",
 96    "source.ip",
 97    "source.geo.country_name",
 98    "event.outcome",
 99    "azure.signinlogs.properties.user_principal_name",
100    "azure.signinlogs.properties.session_id",
101    "azure.signinlogs.properties.app_display_name",
102    "azure.signinlogs.properties.app_id",
103    "azure.signinlogs.properties.resource_display_name",
104    "azure.signinlogs.properties.resource_id",
105    "azure.signinlogs.properties.authentication_protocol",
106    "azure.tenant_id",
107]
108
109[[rule.threat]]
110framework = "MITRE ATT&CK"
111
112[[rule.threat.technique]]
113id = "T1566"
114name = "Phishing"
115reference = "https://attack.mitre.org/techniques/T1566/"
116
117[rule.threat.tactic]
118id = "TA0001"
119name = "Initial Access"
120reference = "https://attack.mitre.org/tactics/TA0001/"
121
122[[rule.threat]]
123framework = "MITRE ATT&CK"
124
125[[rule.threat.technique]]
126id = "T1539"
127name = "Steal Web Session Cookie"
128reference = "https://attack.mitre.org/techniques/T1539/"
129
130[rule.threat.tactic]
131id = "TA0006"
132name = "Credential Access"
133reference = "https://attack.mitre.org/tactics/TA0006/"
Triage and analysis
Investigating Entra ID Potential AiTM Sign-In via OfficeHome (Tycoon2FA)
Review user.name, azure.signinlogs.properties.user_principal_name, azure.signinlogs.properties.app_id, azure.signinlogs.properties.resource_id, user_agent.original, source.ip, source.geo fields, and azure.signinlogs.properties.session_id.
Confirm whether the user intentionally signed in and whether Node.js-style user agents (node, axios, undici) are expected for Microsoft Authentication Broker or Office web client flows in your environment.
Possible investigation steps
- Correlate the session with Microsoft Graph activity logs and mailbox audit for follow-on data access.
- Review conditional access outcomes and MFA detail for the same session.
- Hunt for other sign-ins from the same source IP with unusual user agents or rapid OAuth patterns.
Response and remediation
- If malicious, revoke refresh tokens for the user, reset credentials per policy, and review application consent.
- Block or monitor the source IP and escalate per incident procedures.
References
-
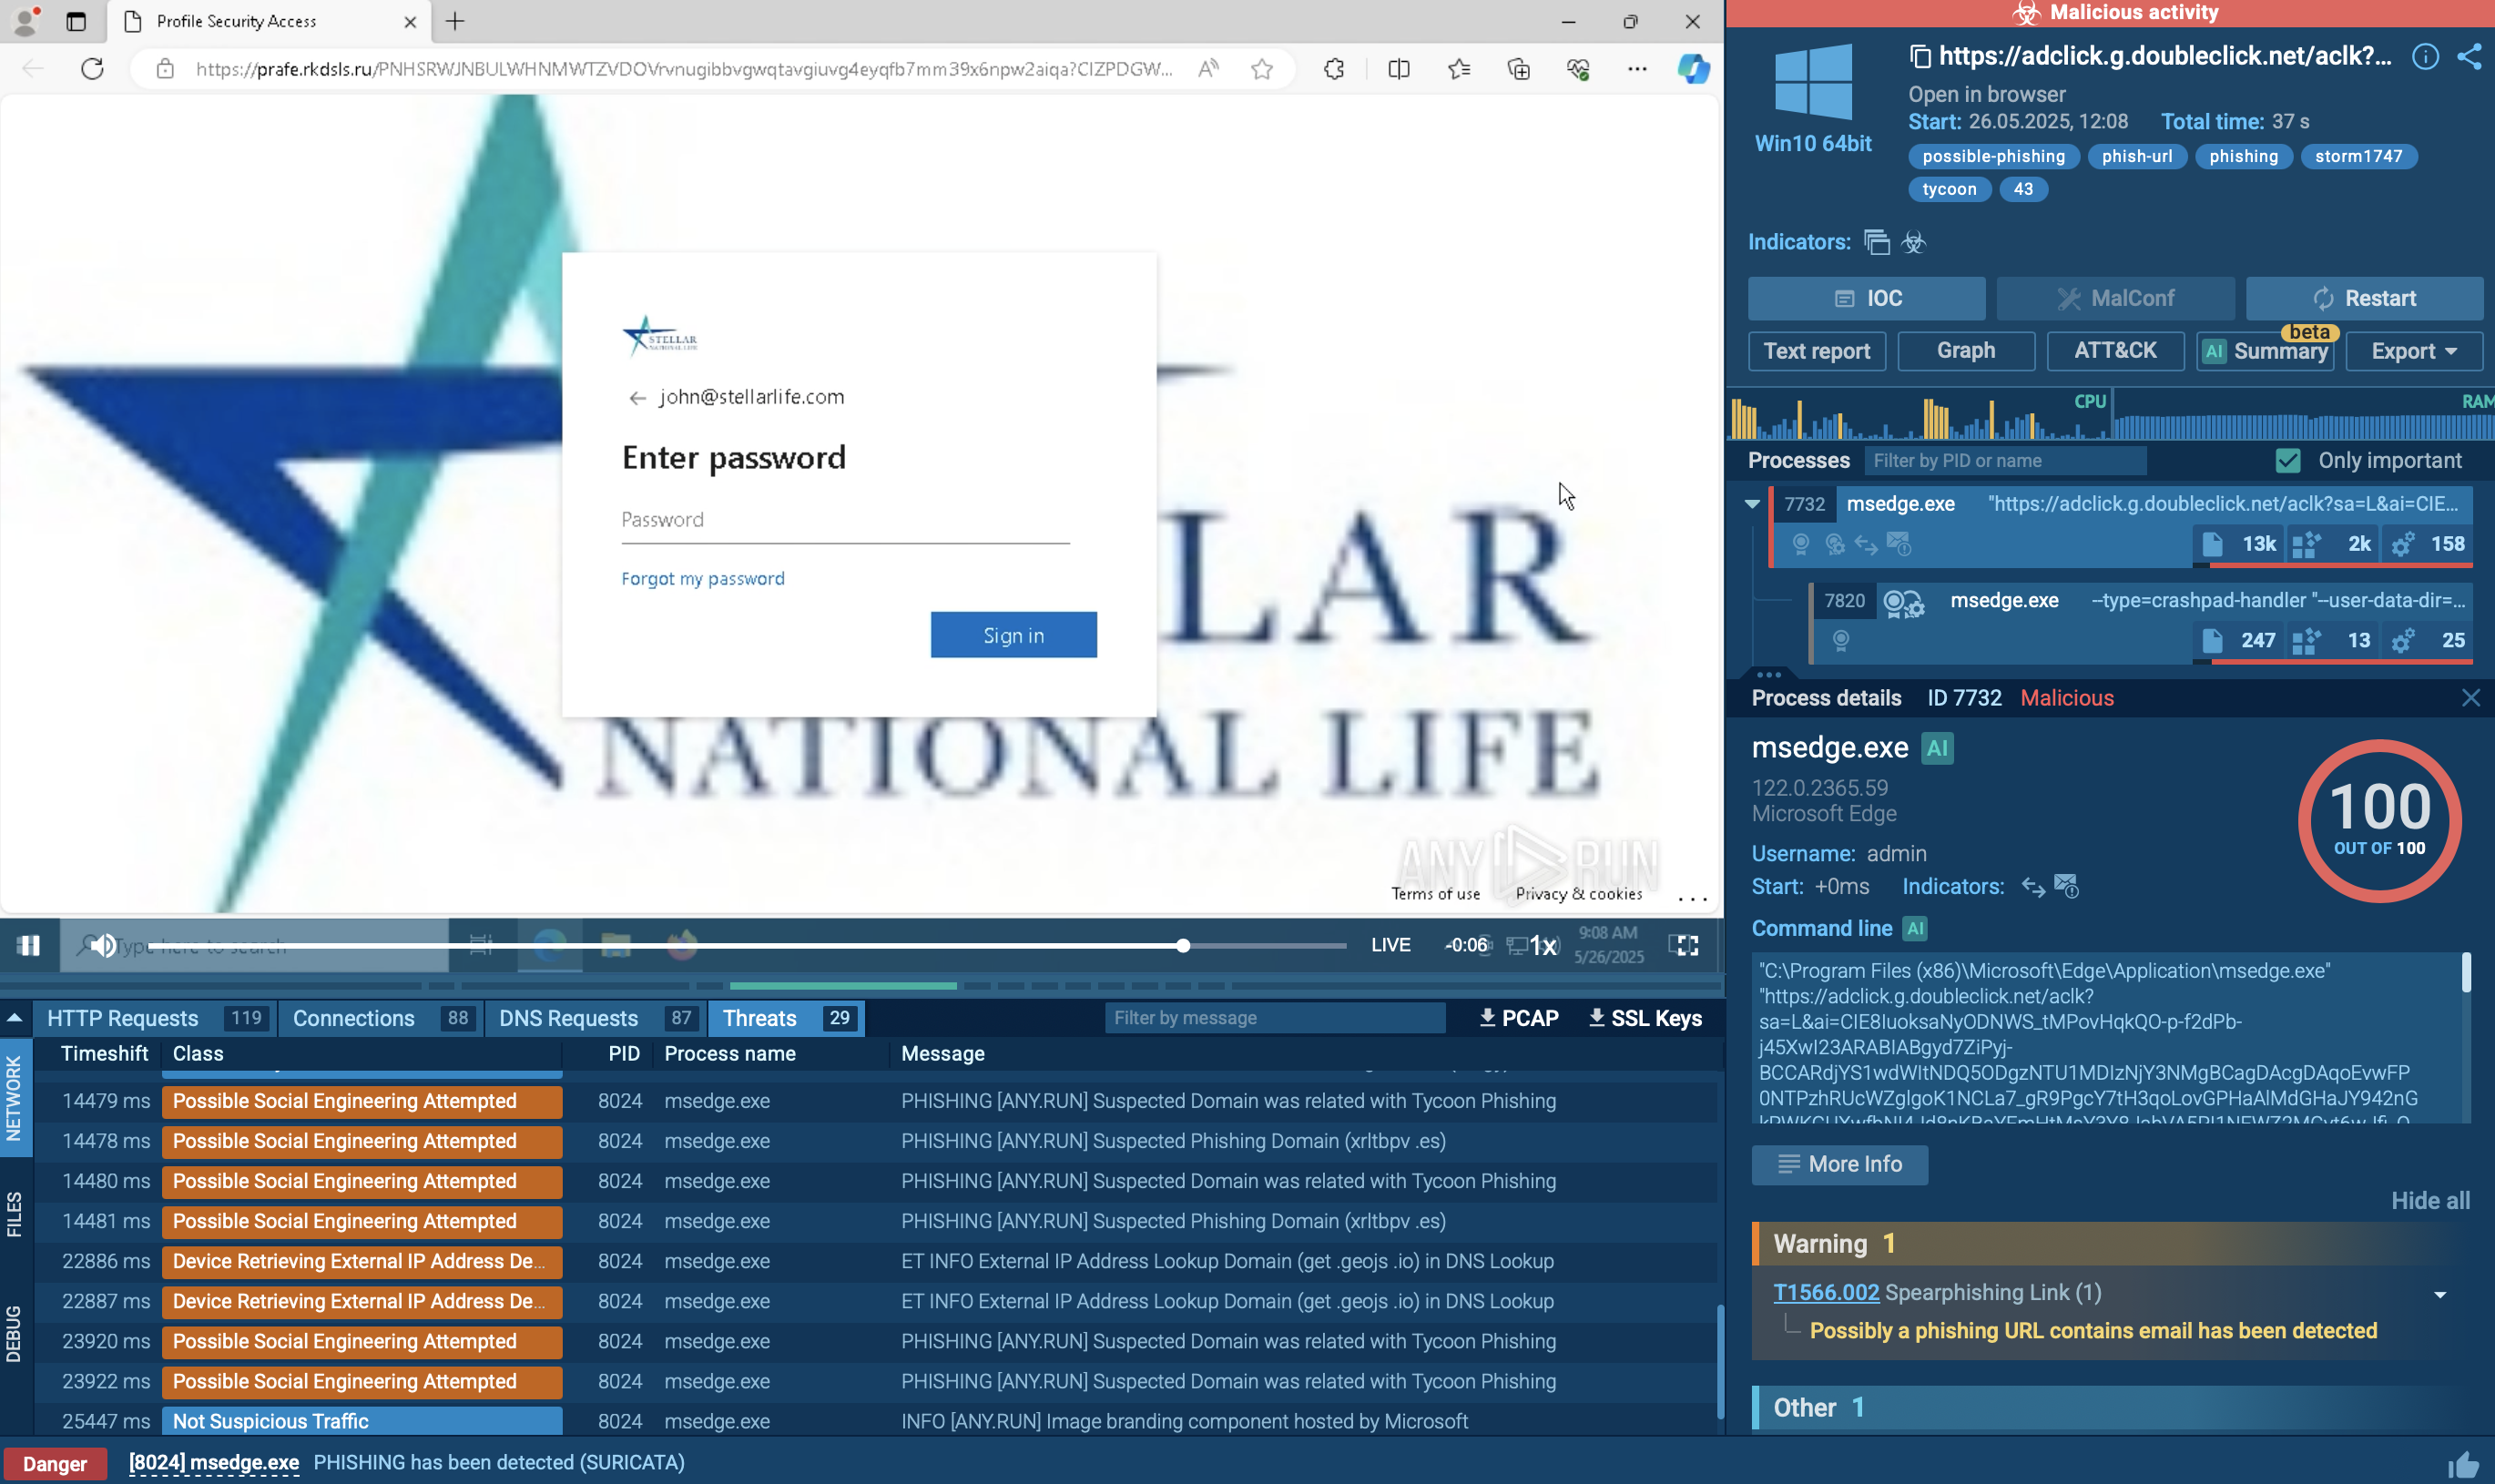
Tycoon 2FA is a phishing-as-a-service kit used for stealing credentials and equipped with advanced evasion capabilities.
Read More
Related rules
- Entra ID Kali365 Default User-Agent Detected
- Entra ID Microsoft Authentication Broker Sign-In with Non-Standard User Agent
- Entra ID Microsoft Authentication Broker DRS Sign-In from Suspicious ASN
- Entra ID Microsoft Authentication Broker Sign-In to Unusual Resource
- Entra ID OAuth Device Code Phishing via AiTM