Excessive Sudo Authentication Failures via macOS Security Events
Identifies a high number of failed sudo password attempts on a macOS host within a short time window, using sudo messages collected by the Authentication data stream of the macOS Security Events integration. Repeated sudo authentication failures may indicate an adversary with access to a low-privileged account attempting to guess an administrator password to escalate privileges.
Elastic rule (View on GitHub)
  1[metadata]
  2creation_date = "2026/09/17"
  3integration = ["macos"]
  4maturity = "production"
  5updated_date = "2026/10/06"
  6
  7[rule]
  8author = ["Elastic"]
  9description = """
 10Identifies a high number of failed sudo password attempts on a macOS host within a short time window, using sudo
 11messages collected by the Authentication data stream of the macOS Security Events integration. Repeated sudo
 12authentication failures may indicate an adversary with access to a low-privileged account attempting to guess an
 13administrator password to escalate privileges.
 14"""
 15from = "now-9m"
 16language = "esql"
 17license = "Elastic License v2"
 18name = "Excessive Sudo Authentication Failures via macOS Security Events"
 19note = """## Triage and analysis
 20
 21> **Disclaimer**:
 22> This investigation guide was created using generative AI technology and has been reviewed to improve its accuracy and relevance. While every effort has been made to ensure its quality, we recommend validating the content and adapting it to suit your specific environment and operational needs.
 23
 24### Investigating Excessive Sudo Authentication Failures via macOS Security Events
 25
 26On macOS, `sudo` prompts for the invoking user's password and, after the configured number of incorrect attempts
 27(three by default), logs a message of the form `<user> : <n> incorrect password attempts ; TTY=<tty> ; PWD=<dir> ;
 28USER=<target> ; COMMAND=<command>` to the unified log. This rule sums the reported attempt counts per host within the
 29rule window and alerts when the total reaches the threshold. The invoking user, target user, TTY, and attempted commands
 30are extracted from the messages and reported in the alert as `Esql.user_name_values`, `Esql.target_user_values`,
 31`Esql.tty_values`, and `Esql.command_values`.
 32
 33### Possible investigation steps
 34
 35- Review `Esql.attempt_total`, `Esql.user_name_values`, and `Esql.command_values` in the alert to identify who was
 36attempting to elevate, how many times, and what they were trying to run.
 37- Determine whether the invoking account is expected to have sudo rights. Failures from an account that is not an
 38administrator suggest privilege escalation attempts rather than mistyped passwords.
 39- Review the attempted commands for reconnaissance, persistence, or credential access tooling (for example, `dscl`,
 40`launchctl`, `security`, `defaults`, shell interpreters, or scripts in user-writable locations).
 41- Check whether a successful sudo invocation by the same user follows the failures in `logs-macos.authentication-*`,
 42which would indicate the password was eventually guessed or known.
 43- Review how the session originated: a local console session (`ttys` with a preceding login window login) versus an SSH
 44session, and correlate with SSH authentication alerts on the same host.
 45- Correlate with other alerts or events from the same host and user during the same period.
 46
 47### False positive analysis
 48
 49- Administrators who mistype their password. The default three-attempt limit per invocation and the threshold make this
 50unlikely from a single interactive session, but repeated invocations can approach it.
 51- Scripts or automation that invoke `sudo` with stale or incorrect credentials in a loop.
 52- Users who are not administrators habitually attempting `sudo`; consider tuning by user or excluding known cases if
 53this is expected behavior.
 54
 55### Response and remediation
 56
 57- Identify the invoking account and its session origin; if the account is not expected to use sudo or the session is
 58remote and unexpected, terminate the session and disable or reset the account.
 59- Review the attempted commands and the host for evidence of prior compromise of the low-privileged account.
 60- Reset the administrator password if there is any indication it may have been guessed or exposed.
 61- Review sudo configuration and administrator group membership on the host; remove unnecessary admin rights.
 62- Escalate to the security operations team if additional hosts show similar patterns.
 63"""
 64references = ["https://themittenmac.com/detecting-ssh-activity-via-process-monitoring/"]
 65risk_score = 21
 66rule_id = "4862d004-3f5f-4ce3-9c83-36cdd5dce8c6"
 67setup = """## Setup
 68
 69This rule requires data from the macOS Security Events integration.
 70Integration setup instructions: [macOS Security Events Integration for Elastic](https://www.elastic.co/docs/reference/integrations/macos)
 71"""
 72severity = "low"
 73tags = [
 74    "Domain: Endpoint",
 75    "OS: macOS",
 76    "Platform: macOS",
 77    "Use Case: Threat Detection",
 78    "Tactic: Privilege Escalation",
 79    "Tactic: Credential Access",
 80    "Data Source: macOS Security Events",
 81    "Rule Type: ESQL",
 82    "Resources: Investigation Guide",
 83]
 84timestamp_override = "event.ingested"
 85type = "esql"
 86query = '''
 87FROM logs-macos.authentication-*
 88| WHERE data_stream.dataset == "macos.authentication" and
 89    macos.process.image_path LIKE "*/sudo" and
 90    macos.event.message.description LIKE "*incorrect password attempt*"
 91| GROK macos.event.message.description "%{NOTSPACE:user_name} : %{NUMBER:attempt_count:int} incorrect password attempt%{DATA} ; TTY=%{NOTSPACE:tty} ; PWD=%{DATA:pwd} ; USER=%{NOTSPACE:target_user} ; COMMAND=%{GREEDYDATA:command}"
 92| STATS
 93    Esql.failure_event_count = COUNT(*),
 94    Esql.attempt_total = SUM(attempt_count),
 95    Esql.user_name_values = VALUES(user_name),
 96    Esql.target_user_values = VALUES(target_user),
 97    Esql.tty_values = VALUES(tty),
 98    Esql.command_values = VALUES(command)
 99  BY host.id, host.name
100| WHERE Esql.attempt_total >= 10
101| KEEP host.id, host.name, Esql.failure_event_count, Esql.attempt_total, Esql.user_name_values, Esql.target_user_values, Esql.tty_values, Esql.command_values
102'''
103
104[[rule.threat]]
105framework = "MITRE ATT&CK"
106
107[[rule.threat.technique]]
108id = "T1548"
109name = "Abuse Elevation Control Mechanism"
110reference = "https://attack.mitre.org/techniques/T1548/"
111
112[[rule.threat.technique.subtechnique]]
113id = "T1548.003"
114name = "Sudo and Sudo Caching"
115reference = "https://attack.mitre.org/techniques/T1548/003/"
116
117[rule.threat.tactic]
118id = "TA0004"
119name = "Privilege Escalation"
120reference = "https://attack.mitre.org/tactics/TA0004/"
121
122[[rule.threat]]
123framework = "MITRE ATT&CK"
124
125[[rule.threat.technique]]
126id = "T1110"
127name = "Brute Force"
128reference = "https://attack.mitre.org/techniques/T1110/"
129
130[[rule.threat.technique.subtechnique]]
131id = "T1110.001"
132name = "Password Guessing"
133reference = "https://attack.mitre.org/techniques/T1110/001/"
134
135[rule.threat.tactic]
136id = "TA0006"
137name = "Credential Access"
138reference = "https://attack.mitre.org/tactics/TA0006/"
Triage and analysis
Disclaimer: This investigation guide was created using generative AI technology and has been reviewed to improve its accuracy and relevance. While every effort has been made to ensure its quality, we recommend validating the content and adapting it to suit your specific environment and operational needs.
Investigating Excessive Sudo Authentication Failures via macOS Security Events
On macOS, sudo prompts for the invoking user's password and, after the configured number of incorrect attempts
(three by default), logs a message of the form <user> : <n> incorrect password attempts ; TTY=<tty> ; PWD=<dir> ; USER=<target> ; COMMAND=<command> to the unified log. This rule sums the reported attempt counts per host within the
rule window and alerts when the total reaches the threshold. The invoking user, target user, TTY, and attempted commands
are extracted from the messages and reported in the alert as Esql.user_name_values, Esql.target_user_values,
Esql.tty_values, and Esql.command_values.
Possible investigation steps
- Review
Esql.attempt_total,Esql.user_name_values, andEsql.command_valuesin the alert to identify who was attempting to elevate, how many times, and what they were trying to run. - Determine whether the invoking account is expected to have sudo rights. Failures from an account that is not an administrator suggest privilege escalation attempts rather than mistyped passwords.
- Review the attempted commands for reconnaissance, persistence, or credential access tooling (for example,
dscl,launchctl,security,defaults, shell interpreters, or scripts in user-writable locations). - Check whether a successful sudo invocation by the same user follows the failures in
logs-macos.authentication-*, which would indicate the password was eventually guessed or known. - Review how the session originated: a local console session (
ttyswith a preceding login window login) versus an SSH session, and correlate with SSH authentication alerts on the same host. - Correlate with other alerts or events from the same host and user during the same period.
False positive analysis
- Administrators who mistype their password. The default three-attempt limit per invocation and the threshold make this unlikely from a single interactive session, but repeated invocations can approach it.
- Scripts or automation that invoke
sudowith stale or incorrect credentials in a loop. - Users who are not administrators habitually attempting
sudo; consider tuning by user or excluding known cases if this is expected behavior.
Response and remediation
- Identify the invoking account and its session origin; if the account is not expected to use sudo or the session is remote and unexpected, terminate the session and disable or reset the account.
- Review the attempted commands and the host for evidence of prior compromise of the low-privileged account.
- Reset the administrator password if there is any indication it may have been guessed or exposed.
- Review sudo configuration and administrator group membership on the host; remove unnecessary admin rights.
- Escalate to the security operations team if additional hosts show similar patterns.
References
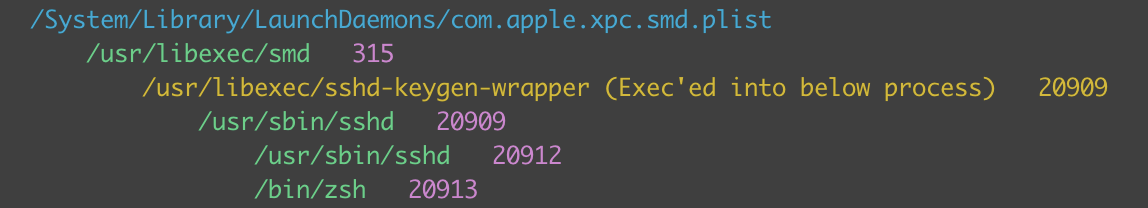
Related rules
- Launch Item Registration with Suspicious Executable Path via macOS Security Events
- Persistence via a Hidden Plist Filename via macOS Security Events
- Potential SSH Brute Force Detected via macOS Security Events
- Potential Successful SSH Brute Force Attack via macOS Security Events
- Privilege Escalation via Parallels Appliance Extract Argument Injection